Failure mode 01
Frameworks that live in documents
A policy set nobody uses, written for an audit that has already passed. Nothing changes at the point where decisions are actually made.
Governance · Risk · Transformation
Board advisoryOntario, CanadaPractising since 2003
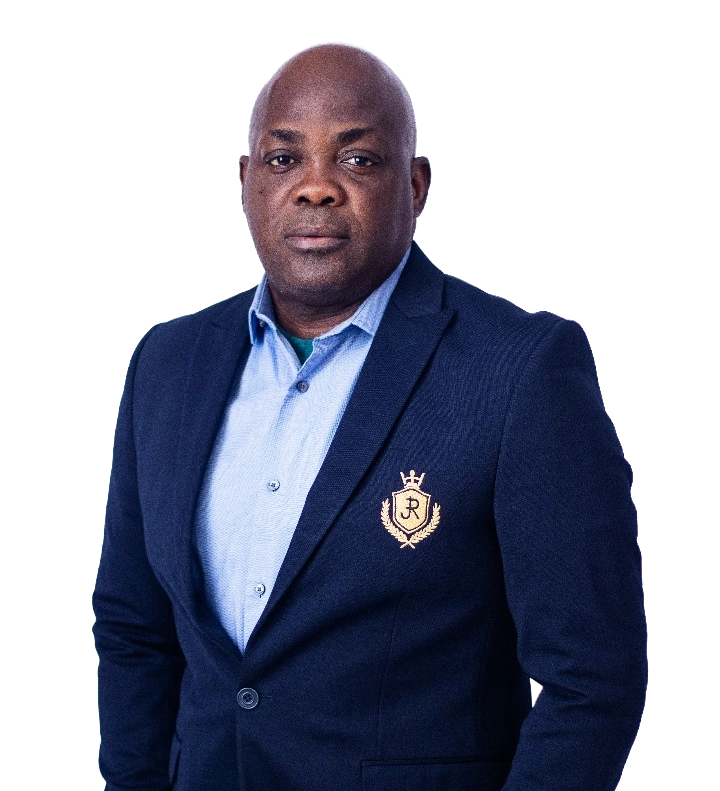
Dr. Orlando Olumide Odejide advises Canadian boards and executive leadership on governance, risk, compliance and cyber resilience, translating Ontario Regulation 51/26, federal cyber law, OSFI expectations and privacy obligations into capability your organization can evidence.
The record
Advisory, assurance and capacity building for Canadian and international organizations, from board charters to certification audits, built on more than twenty years of practice across Africa, Europe and North America.
24+
Years in practiceIndependent advisory across governance, risk, compliance and sustainability since 2003.
40+
CertificationsProfessional credentials across governance, IT, assurance and security.
19
ISO standardsLead Implementer, Lead Auditor and management-system specializations.
18
PracticesStandards-anchored disciplines across two service lines.
The premise
Governance is an operating system, not a binder. The work is to make authority, evidence and accountability visible enough that sound decisions become the default, and then to prove it to a regulator, an auditor, an insurer or a board. In Canada that proof is now being asked for on a clock: maturity assessments, incident reports within 72 hours, resilience testing against fixed dates.
Failure mode 01
A policy set nobody uses, written for an audit that has already passed. Nothing changes at the point where decisions are actually made.
Failure mode 02
Risk recorded but never priced into strategy, capital or delivery. The register is complete and the exposure is unmanaged.
Failure mode 03
Findings raised after the loss, the breach or the disclosure. Assurance becomes reporting rather than protection.
Where the work sits
Each domain is anchored to a recognized standard, so the work is portable, auditable and defensible in front of a regulator, an auditor, an insurer or a board.
Service line 01 · Business GRC
Governance, risk, compliance and sustainability embedded into strategy, decision-making and day-to-day operations, anchored to the ISO standards an auditor, a regulator or an investor already recognizes.
9practices · 11 standards
Service line 02 · IT GRC
Technology governed, managed and secured so it supports business objectives, meets compliance obligations and enables sustainable digital transformation, evidenced against the standards regulators and auditors already use.
9practices · 19 standards
Decision rights, board effectiveness and accountability designed into how the organization actually runs.
ISO 37000Enterprise risk that informs capital, strategy and delivery rather than sitting in a spreadsheet.
ISO 31000Obligations mapped, owned and controlled, with evidence a Canadian regulator would accept without argument.
ISO 37301 · ISO 19011Bribery, whistleblowing and fraud governed as one system rather than three disconnected policies.
ISO 37001 · 37002 · 37003ESG governed as business risk and long-term value, aligned to the SDGs and Canadian disclosure standards.
SDGs · ISO 53001 · CSDSTechnology risk governed as business risk, from service management and cyber resilience through to responsible AI.
ISO 27001 · 22301 · 42001The Canadian horizon
Cyber, privacy, resilience and sustainability obligations have moved from guidance to duty, each with an owner, an assessment and a reporting deadline attached. The work is to answer them as one governance system rather than four separate projects.
In force since 1 July 2026
Regulation 51/26 under the Enhancing Digital Security and Trust Act, 2024 applies to prescribed public-sector entities: colleges and universities, specified public hospitals, school boards and children's aid societies. They must run a cybersecurity program, designate senior cybersecurity contacts, carry out recurring maturity assessments, report results and improvement opportunities, and report a confirmed critical incident within 72 hours.
The executive question is no longer whether the technology is adequate. It is whether cybersecurity can be shown to be governed, assessed, managed, monitored and continuously improved. NIST CSF 2.0 gives that answer an architecture.
O. Reg. 51/26 · NIST CSF 2.0
Cybersecurity programs, maturity assessments and 72-hour incident reporting for prescribed Ontario entities.
Bill C-8 (ARCS) · CCSPA
Federal cyber law received Royal Assent in June 2026, with CCSPA obligations for designated operators phasing in by order in council.
OSFI E-21 · B-13 · B-10
Critical operations mapped, impact tolerances set, third-party and technology risk governed, scenario testing evidenced.
PIPEDA · Law 25 · PHIPA · FIPPA
Federal, Quebec, health and public-sector privacy duties handled as one accountability framework rather than four.
CSDS 1 & 2 · OSFI B-15 · ISO 53001
Canadian Sustainability Disclosure Standards governed with the controls and evidence that assurance will eventually require.
ISO 42001 · NIST AI RMF
AI systems classified, assessed and governed across the lifecycle, ahead of the Canadian rules now taking shape.
ISO 37001 · 37002 · 37003
Anti-bribery, whistleblowing and fraud governed as one system, aligned to Canadian conduct and supply-chain expectations.
ISO 37000 · 31000 · 37301
The governing spine: decision rights, enterprise risk and compliance obligations owned, controlled and auditable.
Regulatory positions change. This page states a management interpretation, not legal advice; organizations should confirm applicable requirements and current Ministry, OSFI and regulator guidance before acting.
The register
Filter by service line or search by standard. Open any practice for its full scope, deliverables and business case.
No practice matches that search. Try a standard number, or reset the filters.
Board readiness diagnostic
Answer as your board would answer, not as the policy says. The result names your maturity band and the three practices that would move it fastest.
How engagements run
The same sequence whether the subject is a board charter, a Regulation 51/26 readiness review, an ISMS or an AI management system. It ends when your people can run it without us.
Regulatory readiness review and a current-state assessment against the applicable standard.
Governance, people, process, technology, reporting and resilience gaps named and sized.
Target profile, priorities, owners, investment, milestones and performance indicators.
Controls, policies, structures and skills built where decisions are actually made.
Evidence maintained, maturity measured, readiness tested and capabilities reassessed.
Where it applies
The standard is constant. The regulator, the risk appetite and the failure mode are not.
Regulation 51/26 cybersecurity programs, maturity assessments, incident reporting and research-data governance.
PHIPA obligations, clinical system continuity, third-party risk and privacy accountability.
Prescribed-entity cyber duties, student data protection and board-level oversight that survives turnover.
OSFI E-21, B-13 and B-10 expectations, conduct risk, operational resilience and third-party oversight.
FIPPA and MFIPPA accountability, procurement integrity and institutional capacity across political cycles.
Critical cyber systems, ESG disclosure and operational risk across long, regulated supply chains.
Federal cyber obligations, service continuity, cloud governance and responsible AI deployment.
Funder accountability, fraud control, whistleblowing systems and SDG alignment.
Frameworks, books and training
The same standards-led thinking, available as leadership retreats, books, accredited training and practice partnerships.
Retreats
Engineering organizational strength, stability and longevity. Activity is not progress. Sales is not strength. Growth is not endurance.
Explore the retreatsBooks
Training
Ninety-six accredited sessions across ISO management systems, ITIL 5 and professional practice, scheduled every month of the year.
Find your coursePartnerships
Build an IT-GRC and digital transformation practice without building it from scratch, using proven curriculum, certified faculty and ready methodologies.
See the partnership modelsIn their words
Clients, colleagues and the professionals trained across two decades of practice.
A transformational leader whose work spans management consulting, enterprise development and capacity building. Over two decades, he has consistently championed excellence, innovation and global best practices across industries.
He has a remarkable ability to spot raw talent in places most people overlook, people who don't realise their own potential, and he nurtures them with patience, guidance and belief.
A remarkable mix of passion, wisdom and genuine love for people. His steady professional guidance and constant kindness have changed lives in ways words can hardly capture.
Brilliant but still humble, visionary yet grounded. He has a way of making the impossible feel possible, and everyone who works with him walks away better than they came.
A strong reputation as a consultant, trainer and transformation expert who genuinely understands how to help people and organizations grow.
Insights
On cyber resilience, wicked problems and the discipline of governing well.
Briefing · Ontario
Article · SDGs
Article · Capability
Start the conversation
Bring the obligation you are least able to evidence today. We will name where the gap actually sits, what closing it involves, and whether it is work you need help with at all.
Work with Dr. Orlando Olumide Odejide
Ready to strengthen governance, risk and compliance across your organisation?
© 2026 Dr. Orlando Global Projects. All rights reserved.
Designed and Developed by RCT
People · Standards · Performance